Buenos Aires, Argentina • Active in Cyber Defense & DFIR

Paula Villegas

Cybersecurity Analyst • SOC & Incident Response • DFIR Enthusiast

Over 3.5 years of specialized experience in Security Operations Centers (SOC) collaborating with international teams in 24/7 monitoring, phishing triage, and incident response. Driven by a passion for Digital Forensics and Incident Response (DFIR), Human-AI defense collaboration, and community mentorship.
3.5+
Years of SOC Experience
BTL1 • Cortex XDR
Verified Certifications
Ekoparty 2025
Featured Conference Speaker
GPA 3.7
Computer Engineering (UNAJ)
SECTION 01

About Me

My professional journey across high-tempo SOC environments, engineering education, technical skillset, and defensive certifications.

Professional Summary

I am a Cybersecurity Analyst with three and a half years of specialized experience in SOC environments, collaborating alongside multinational teams to deliver robust threat monitoring, alert triage, and incident response.

My technical focus is propelled by a deep interest in Digital Forensics and Incident Response (DFIR) and the emerging synergy between AI agents and human analysts to accelerate triage without sacrificing forensic integrity.

Deeply committed to continuous learning, I actively contribute to cybersecurity communities, lead mentoring initiatives for women in cyber defense, and speak at conferences to share knowledge and foster resilient digital ecosystems.

🎓
Computer Engineering Degree
Universidad Nacional Arturo Jauretche (2021 — Present)
GPA 3.7 • 18 subjects passed
💻
Programmer Analyst Intermediate Degree
Strong foundations in algorithms, databases, and multi-language development
Nearing completion
Security & Growth Mindset:
"Effective defense requires proactive curiosity, relentless attention to anomalous signals, and empowering the community through shared knowledge."
🇪🇸 Spanish: Native 🇬🇧 English: Advanced (B2) 🇯🇵 Japanese: Basic (JLPT N5)

Technical Competencies

  • SIEM / SOAR Monitoring & Orchestration

    Splunk SIEM, Splunk SOAR, Cortex, OSSIM, FortiSIEM. Alert correlation, triage pipelines, and case lifecycle management.

  • XDR & EDR Endpoint & Extended Detection

    Palo Alto Cortex XDR, Microsoft Defender, Trend Micro. Process inspection, containment, and endpoint telemetry.

  • DFIR & OSINT Investigation & Reconnaissance

    Nessus vulnerability assessments, Maltego graph analysis, open-source intelligence (OSINT), and network traffic analysis.

  • DEV & DATA Databases & Programming

    SQL, NoSQL, Python (basic scripting & automation), Java, C#, JavaScript. Foundations in software development lifecycle.

Career Trajectory Timeline

A chronological progression of operational experience, responsibilities, and team impact.

Cybersecurity Analyst

CYBER42
October 2025 — Present
  • Monitor security events and execute structured incident response procedures leveraging Human-AI collaboration.
  • Manage enterprise ticketing systems for comprehensive, auditable case tracking and root-cause documentation.
  • Collaborate actively with global engineering and defense teams on complex case investigations and active phishing analysis.
  • Utilize enterprise detection tools including Microsoft Defender, Cortex XDR, and Trend Micro.
Human-AI Collaboration Cortex XDR Microsoft Defender Trend Micro Phishing Analysis Incident Response

Security Delivery Associate

Accenture AR • Global Operations
January 2024 — October 2025
  • Monitored, triaged, and prioritized high-volume security alerts utilizing Splunk SIEM and Splunk SOAR.
  • Maintained incident management systems to ensure swift ticket escalation and strict SLA adherence.
  • Applied actionable threat intelligence and newly released vulnerability reports directly into internal monitoring playbooks.
  • Collaborated closely with global L2 analysts for in-depth forensics, investigations, and incident resolution.
  • Facilitated onboarding, technical training, and mentoring support for new incoming team members.
Splunk SIEM Splunk SOAR Threat Intelligence L2 Collaboration Playbook Optimization Team Mentorship

Cybersecurity Analyst (CSIRT)

Ministry of Security of Argentine Nation
June 2023 — January 2024
  • Monitored and investigated critical security incidents leveraging OSSIM and FortiSIEM platforms.
  • Conducted systematic vulnerability assessments utilizing Nessus and OSINT reconnaissance techniques.
  • Executed front-line incident response, event triage, and authored detailed technical briefing reports on findings.
OSSIM FortiSIEM Nessus OSINT CSIRT Response Government Defense

Education & Professional Certifications

BTL1

Blue Team Level 1

Security Blue Team

August 2025 • Verified
CORTEX

Cortex XDR: Features

Palo Alto Networks

October 2025 • Verified
AND

Investigation Theory

Applied Network Defense

September 2024 • Verified
CISCO

Networking Basics

Cisco Networking Academy

January 2025 • Verified
FORTINET

FCF & FCA Certifications

Fortinet Training Institute

November 2023 • Verified
UNAJ

Computer Engineering (Degree)

Univ. Nac. Arturo Jauretche

GPA 3.7 • 2021 — Present

Microsoft Learn • Badges & Achievements

Continuous technical skilling in cybersecurity operations, threat protection, and Microsoft Defender / Azure architectures.

View Microsoft Badges
SECTION 02

Technical Projects

Defensive engineering implementations, incident response tooling, detection correlation, and programming foundations.

Technical Research CYBER42 • Active

Human-AI Collaboration in SOC Incident Response

Implementing and evaluating AI-assisted workflows in live SOC environments to automate first-pass phishing categorization, IOC extraction, and log aggregation while keeping seasoned analysts in the loop for nuanced forensic validation.

Accelerated Triage • Forensic Integrity Maintained
AI Agents Cortex XDR Phishing Automation Human-in-the-Loop
Defense Engineering Accenture AR • CSIRT

Multi-Platform SIEM Alert Correlation & Threat Intel

Operational expertise across Splunk, OSSIM, and FortiSIEM integrating real-time vulnerability advisories and threat intelligence feeds into detection rules, false-positive reduction routines, and enterprise escalation paths.

Splunk • FortiSIEM • OSSIM • Threat Intel Ingestion
Splunk SIEM Splunk SOAR FortiSIEM Threat Intel
Software & Scripting UNAJ • Programmer Analyst

Programmer Analyst Foundations & Automation

Developing automation tools and investigative scripts leveraging Python, Java, C#, and SQL/NoSQL databases. Bridging the gap between software engineering architecture and defensive security controls.

UNAJ Computer Engineering • Full SDLC & Algorithms
Python Java C# SQL / NoSQL JavaScript
SECTION 03

Community & Initiatives

Conference keynote speaking, mentorship for women in cybersecurity, educational content creation, and community leadership.

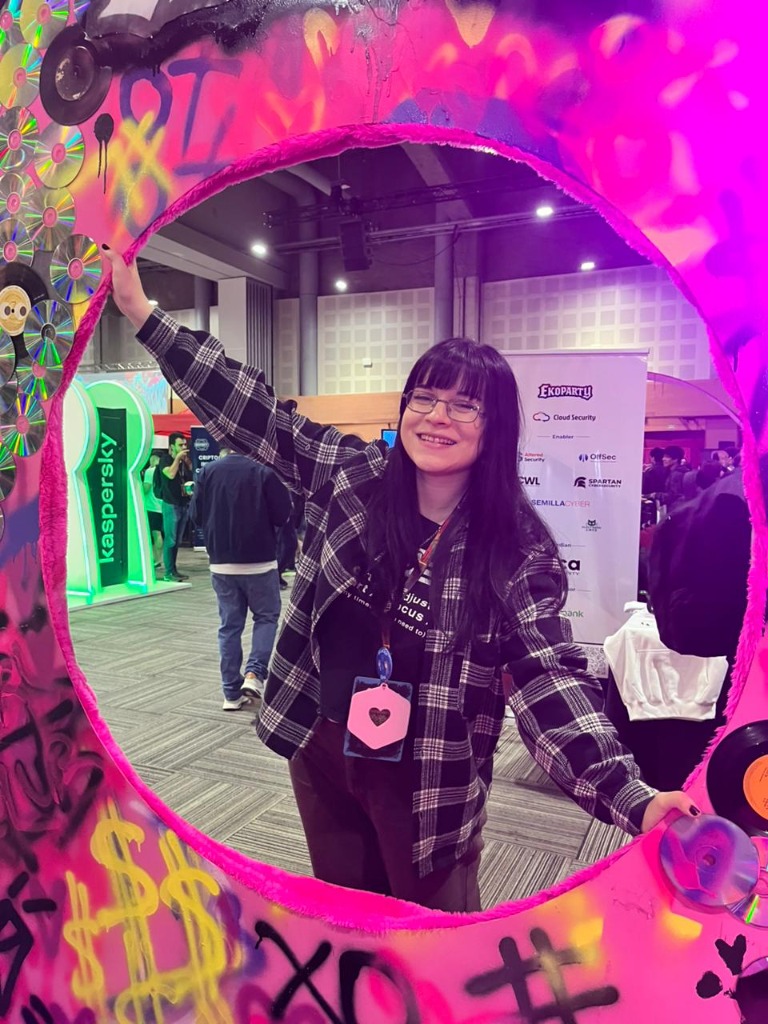
Paula Angeles Villegas speaking at Ekoparty 2025
Ekoparty 2025
Conference Speaker Ekoparty 2025

"Press Play: Level One of the Professional World"

Delivered a featured conference talk at Ekoparty 2025 focusing on career onboarding in cybersecurity, breaking into blue teaming, navigating technical growth curves, and turning entry-level SOC roles into long-term defensive trajectories.

★ Ekoparty 2025 Speaker • Career Navigation & Blue Team Entry
Public Speaking Conference Talk Career Onboarding Ekoparty
Mentorship & Community Active Volunteer

Bug Bounty Girls Club & Women Hacks Panel

Active volunteer at Bug Bounty Girls Club, co-creating technical content and mentoring women in Cyber Defense through the BlueOps Girls initiative. Selected to participate in the prestigious Women Hacks panel at Ekoparty 2026 representing the club to foster diversity in threat analysis and defensive engineering.

★ Women Hacks Panel @ Ekoparty 2026 • BlueOps Girls Mentor
Bug Bounty Girls Women Hacks Panel Ekoparty 2026 BlueOps Girls Cyber Defense Mentorship
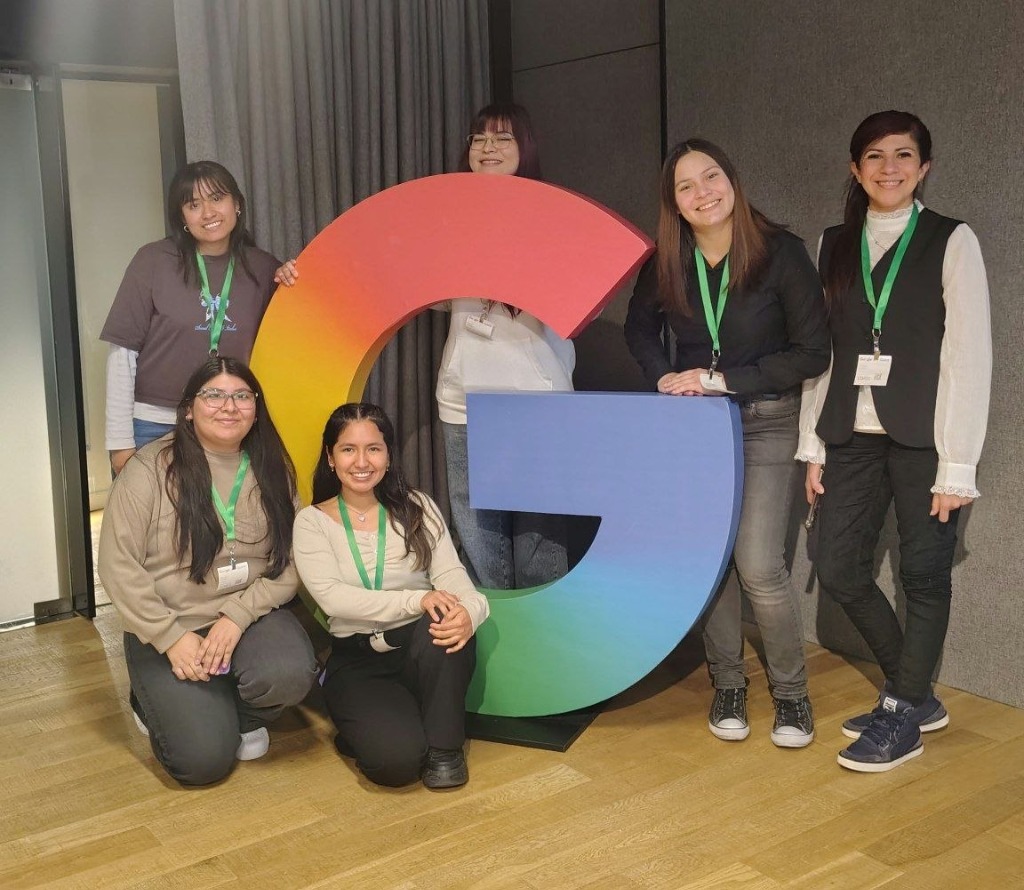
Paula Villegas with SteamGirls community at Google
SteamGirls
Community & Diversity SteamGirls Community

SteamGirls Community & Cyber Empowerment

Active participant in the SteamGirls community, contributing to initiatives that empower women across STEAM disciplines and cybersecurity. Collaborating on networking, technical sessions, and community events at Ekoparty to support upcoming talent.

★ SteamGirls Member • STEAM & Cyber Empowerment
SteamGirls Women in STEAM Ekoparty Diversity in Tech Networking
Content Creation & Education Instagram @pua.blue

@pua.blue • Cybersecurity Content & Blue Teaming

Creator of @pua.blue, an educational cybersecurity initiative on Instagram sharing insights on Blue Teaming, SOC operations, DFIR fundamentals, threat hunting, and encouraging women and newcomers to thrive in cyber defense.

★ Educational Infosec Channel • Community Growth & Defense Tips
Cyber Education Blue Teaming DFIR Concepts Community Outreach Instagram
COMMUNICATIONS

Get in Touch

Interested in discussing SOC/DFIR opportunities, speaking invitations, or community mentorship? Send a message directly to my inbox below.

Send a Direct Message

Your email address is only used to reply to your inquiry. Messages are delivered straight to my personal inbox.

Bot-Protected Dispatch
GitHub Profile
@PuaBlue
Public security repos & code
Microsoft Learn
paulavillegas-3482
Verified badges & skilling achievements
LinkedIn Profile
/in/puasec
Connect, network, & view recommendations
Instagram (Content)
@pua.blue
Cybersecurity education & defensive tips
Location & Work Mode
●
Buenos Aires, Argentina
Open to remote & international engagements
Privacy & Security Note

Direct plaintext emails are obscured to mitigate automated bot scrapers and phishing harvesters. All submissions route securely to Paula's authenticated inbox.